Attribute Injection leading to XSS(Cross-Site-Scripting)GHSA-v4v2-8h88-65qj
MEDIUMFix: louislam/uptime-kuma@f28dccfGHSA-v4v2-8h88-65qj is a medium-severity (CVSS 6.1) Cross-site Scripting (XSS) vulnerability in uptime-kuma. 1 public exploit or proof-of-concept reference is indexed, so weaponization risk is real. A fix is available for uptime-kuma — see the affected versions and patch details below.
EPSS Exploitation Probability
Probability of exploitation in the next 30 days, from FIRST.org EPSS.
How urgent is this, really
Where this sits among everything scored
Real-World Exposure
How broadly this vulnerability is actually deployed: weekly install volume shows current usage, and reverse-dependency count shows how many other packages break if it stays unpatched.
uptime-kumanpmDescription
Summary
Google Analytics element Attribute Injection leading to XSS
Details
Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks.
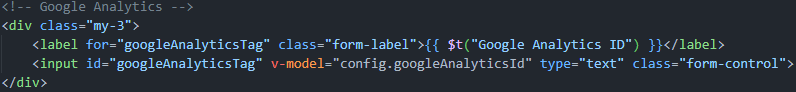
PoC
- Run the latest version of the louislam/uptime-kuma container and initialize the account password.
- Create a new status page.
- Edit the status page and change the Google Analytics ID to following payload(it only works for firefox. Any attribute can be injected, but this seems the most intuitive):
123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="x
- Click Save and return to the interface. XSS occurs.
screenshots:


Affected Packages
| Ecosystem | Package | Vulnerable range | Fix |
|---|---|---|---|
| 📦npm | uptime-kuma | ≥ 1.20.0&&< 1.23.7 | 1.23.7npm install uptime-kuma@1.23.7 |
Affected Products
uptime kumauptime.kumaResearch use only. For defensive security, authorized penetration testing, and academic research only. Never execute exploit code against systems without explicit written authorization.
Detection & mitigation playbook
Open-source dependencyDetect
Scan your dependency tree (package-lock.json, pnpm-lock.yaml, requirements.txt, go.sum, etc.) for uptime-kuma, including transitive dependencies — a direct dependency you never call can still pull in a vulnerable version.
Fix
Update uptime-kuma to 1.23.7 or later, then make sure no transitive (indirect) dependency still pins the vulnerable range — O3 confirms GHSA-v4v2-8h88-65qj is resolved across your whole dependency graph.
Workarounds
Escape or sanitise the affected output on the server side rather than relying on client-side filtering, and add a Content-Security-Policy that blocks inline script execution so injected markup cannot run even if it reaches the page.
Frequently Asked Questions
Is GHSA-v4v2-8h88-65qj in your dependencies?
Find it across npm, including transitive dependencies.