CVE-2026-52796 is a low-severity (CVSS 3.5) CWE-1336 vulnerability in gogs.io/gogs. A fix is available for gogs.io/gogs — see the affected versions and patch details below.
Gogs: DoS in rendering issue index pattern
Exploitation Status
Proof-of-concept exploit code exists
- CISA’s SSVC triage found public proof-of-concept exploit code for this CVE, though no confirmed active exploitation.
Exploitation and automatability from CISA’s SSVC triage for CVE-2026-52796.
EPSS Exploitation Probability
Probability of exploitation in the next 30 days, from FIRST.org EPSS.
How urgent is this, really
CVE-2026-52796 by exploitation likelihood (EPSS) against impact (CVSS). Outside the shaded patch-first corner.
Where this sits among everything scored
Of 395,249 CVEs with a current EPSS score, this one falls in the < 10% band (highlighted). Counts from FIRST.org, log-scaled.
Real-World Exposure
gogs.io/gogsReal-time download stats are indexed for npm and PyPI packages. This vulnerability affects Go packages — download data is not available via public APIs for these ecosystems.
Description
Summary
Special template of issue index pattern may cause panic.
Details
in internal/markup/markup.go
link = fmt.Sprintf(`<a href="%s">%s</a>`, com.Expand(metas["format"], metas), m)
Issue index pattern is rendered to link with com.Expand.
However, com.Expand is not safe.
i = strings.Index(template, "}")
if s, ok := match[template[:i]]; ok {
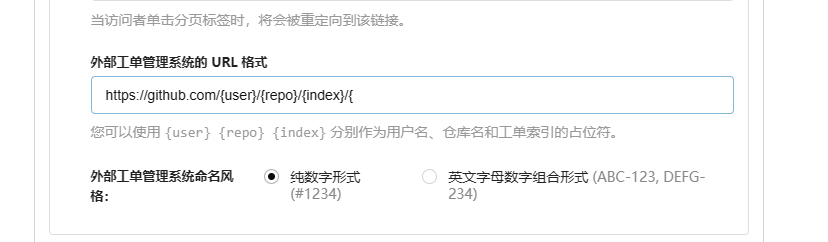
when { is found but } not found, i comes to 1, template[:-1] will be called, and then panicked
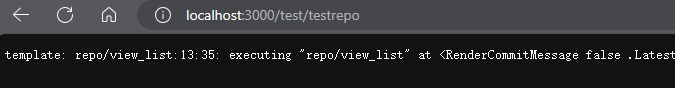
finally, all pages than contains issue index are unavailable.
PoC
- set issue index pattern as follow
- add a commit which point to an issue in its msg
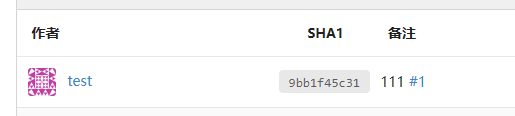
using #1 above
Impact
DoS that cause part of pages of the specify repo unavailable.
Affected Packages
| Ecosystem | Package | Vulnerable range | Fix |
|---|---|---|---|
| 🐹Go | gogs.io/gogs | all versions | 0.14.3go get gogs.io/gogs@v0.14.3 |
Detection & mitigation playbook
Open-source dependencyDetect
Scan your dependency tree (package-lock.json, pnpm-lock.yaml, requirements.txt, go.sum, etc.) for gogs.io/gogs, including transitive dependencies — a direct dependency you never call can still pull in a vulnerable version.
Fix
Update gogs.io/gogs to 0.14.3 or later, then make sure no transitive (indirect) dependency still pins the vulnerable range — O3 confirms CVE-2026-52796 is resolved across your whole dependency graph.
Workarounds
Cap what an attacker can consume: apply request size, rate and timeout limits in front of the affected component, and run it with memory and CPU limits so exhaustion degrades one worker rather than the whole service.
Frequently Asked Questions
Is CVE-2026-52796 in your dependencies?
Find it across Go, including transitive dependencies.