CVE-2025-32963 — operator
Fix: minio/operator@d586294CVE-2025-32963 is a CWE-522 vulnerability in github.com/minio/operator. A fix is available for github.com/minio/operator — see the affected versions and patch details below.
Minio Operator uses Kubernetes apiserver audience for AssumeRoleWithWebIdentity STS
Exploitation Status
No confirmed exploitation observed yet
- CISA assesses this as automatable — exploitation doesn’t require manual, per-target effort, which raises the odds of mass scanning and opportunistic attacks.
- CISA’s own triage has not observed active exploitation or public proof-of-concept code for this CVE as of its last assessment.
Exploitation and automatability from CISA’s SSVC triage for CVE-2025-32963.
EPSS Exploitation Probability
EPSS (Exploit Prediction Scoring System) is a daily probability model maintained by FIRST.org. It estimates the likelihood a CVE will be exploited in production environments within the next 30 days, derived from real-world threat intelligence signals.
Real-World Exposure
github.com/minio/operatorReal-time download stats are indexed for npm and PyPI packages. This vulnerability affects Go packages — download data is not available via public APIs for these ecosystems.
Description
Prevent token leakage / privilege escalation
MinIO Operator STS: A Quick Overview
MinIO Operator STS is a native IAM Authentication for Kubernetes. MinIO Operator offers support for Secure Tokens (a.k.a. STS) which are a form of temporary access credentials for your MinIO Tenant. In essence, this allows you to control access to your MinIO tenant from your applications without having to explicitly create credentials for each application.
For an application to gain access into a MinIO Tenant, a PolicyBinding resource is required, granting explicit access to the applications by validating the kubernetes Service Account authorization token.
The service account token is validated as follows:
- The application calls
AssumeRoleWithWebIdentityAPI MinIO Operator provides. - MinIO Operator verifies the Service Account token agains the kubernetes API using the TokenReview API
- MinIO Operator reviews the TokenReviewResult confirms if the token is a valid token and the user is authenticated.
- MinIO Operator validates the service account has
PolicyBindingin the Tenant namespace. - MinIO Operator gets the PolicyBinding
- MinIO Operator calls the AssumeRole API in the MinIO Tenant
- MinIO Operator obtains temporary credentials (STS).
- MinIO Operator return temporary Credentials to the requester application.
- The applicaiton consumes Object Storage using the temporary credentials.
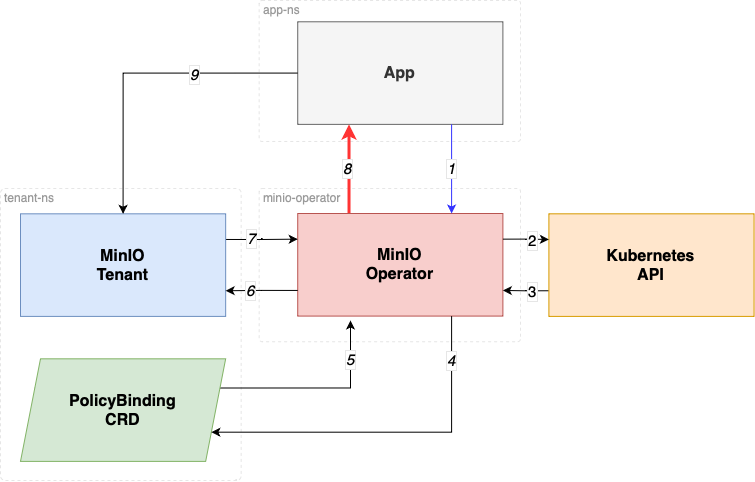
Understanding Audiences in Kubernetes TokenReview
In step 2 the TokenReview API call attempts to authenticate a token to a known user, TokenReviewStatus is the result of the TokenReview request.
Audiences are audience identifiers chosen by the authenticator that are compatible with both the TokenReview and token.
An identifier is any identifier in the intersection of the TokenReviewSpec audiences and the token's audiences.
A client of the TokenReview API that sets the spec.audiences field should validate that a compatible audience identifier is returned in the status.audiences field to ensure that the TokenReview server is audience aware.
If no audiences are provided, the audience will default to the audience of the Kubernetes apiserver.
Solution: Properly Issuing and Using Audience-Specific ServiceAccount Tokens
This PR ensures the Operator STS service request the Service Account JWT to belong to the audiencests.min.io in the TokenReviewRequest.
This PR ensures the examples and documentation provided guides in how to create Service accounts with "disabled auto mount services tokens", by doing this the pods where the service account is used no longer mounts the service account automatically in the path /var/run/secrets/kubernetes.io/serviceaccount.
For illustrative purposes, here is how you disable auto mount of service account tokens at the service account level.
apiVersion: v1
kind: ServiceAccount
metadata:
  namespace: namespace-name
  name: service-account name
automountServiceAccountToken: false
Additionally documentation and examples show how to request an audience-specific token with audience sts.min.io, by asking for an ServiceAccount Token to be audience specific.
For illustrative purposes, here is how you request an audience specific service account token in a pod:
apiVersion: batch/v1
kind: Job
metadata:
  name: job-name
  namespace: job-namespace
spec:
  template:
    spec:
      serviceAccountName: service-account-name
      volumes:
        - name: sa-token
          projected:
            sources:
              - serviceAccountToken:
                  audience: "sts.min.io"
                  expirationSeconds: 86400
                  path: token
      containers:
        - name: mc
...
          volumeMounts:
            - name: sa-token
              mountPath: /var/run/secrets/sts.min.io/serviceaccount
              readOnly: true
How this prevent a token leakage or possible privilege escalation?.
This setup prevents privilege escalation and token leakage by combining multiple defense-in-depth mechanisms that ensure service account tokens are only usable by their intended audience, short-lived, and not exposed unnecessarily.
Audience restriction (aud: sts.min.io)
Problem: A ServiceAccount token is often valid for multiple audiences (e.g., the default Kubernetes API server). Without scoping, it can be replayed to other internal systems, which may unintentionally trust it.
Mitigation: Now we enforce that tokens are explicitly created for the sts.min.io audience using the Kubernetes TokenRequest API, and the MinIO Operator:
Sends audiences: ["sts.min.io"] in the TokenReview.
Verifies that the token was issued with this audience via status.audiences.
Effect: Even if a token is stolen or misused, it will fail validation if used outside the sts.min.io STS endpoint (e.g., reused at the API server or another service).
Token Leakage Mitigation
Disabling auto-mounted service account tokens
Problem: By default, Kubernetes mounts long-lived service account tokens into all pods at /var/run/secrets/kubernetes.io/serviceaccount, making them vulnerable to theft if the container is compromised.
Mitigation: No we guide users to set automountServiceAccountToken: false in their ServiceAccount definitions.
Effect: Prevents automatic token injection into all pods, reducing the attack surface.
Requesting short-lived, audience-specific tokens via serviceAccountToken projection
Problem: Long-lived tokens can be reused indefinitely if leaked. Mitigation: You use projected service account tokens with:
- audience: "sts.min.io"
- A short expirationSeconds (e.g., 86400 = 24 hours, or even shorter)
Effect: Even if the token is leaked, it is:
- Only usable for sts.min.io
- Short-lived and expires soon
- Revocable by disabling the SA or STS access
Affected Versions and Risk Assessment
The issue affects MinIO Operator versions v5.0.x and above, when the STS feature was first introduced.
- In v5.0.x, STS was introduced as v1alpha1 and disabled by default. It required explicit API calls to be used.
- In v6.0.x, STS graduated to v1beta1 and was enabled by default, but still requires explicit calls to the STS API for token usage.
The risk is minimal, as:
- The Operator does not persist the token (neither in memory nor on disk).
- The Operator only uses the token for a single validation and does not reuse it for any other purpose.
Release
Fix released in v7.1.0
Affected Packages
| Ecosystem | Package | Vulnerable range | Fix |
|---|---|---|---|
| 🐹Go | github.com/minio/operator | all versions | 7.1.0go get github.com/minio/operator@v7.1.0 |
Detection & mitigation playbook
Open-source dependencyDetect
Scan your dependency tree (package-lock.json, pnpm-lock.yaml, requirements.txt, go.sum, etc.) for github.com/minio/operator, including transitive dependencies — a direct dependency you never call can still pull in a vulnerable version.
Fix
Update github.com/minio/operator to 7.1.0 or later, then make sure no transitive (indirect) dependency still pins the vulnerable range — O3 confirms CVE-2025-32963 is resolved across your whole dependency graph.
Workarounds
If you can't upgrade right away: gate or disable the affected feature, validate untrusted input at the boundary, and avoid passing attacker-controlled data into the vulnerable path. O3's runtime protection blocks exploitation in production as an interim safeguard until the upgrade lands.
How O3 protects you
O3 Security's impact-aware SCA analyses which vulnerable code paths your application actually calls, so a match like CVE-2025-32963 can be triaged on real exposure rather than presence alone.
Tailored to CVE-2025-32963. Runtime protection reduces exposure until a permanent patch is applied and verified — it complements patching, it doesn't replace it.
Frequently Asked Questions
Is CVE-2025-32963 in your dependencies?
O3 Security finds CVE-2025-32963 across Go dependencies, including transitive ones, and its impact-aware SCA ranks findings by whether your code actually calls the vulnerable path.